Shadow AI Has Become a Behavioral Data-Movement Risk
89% of workplace AI use escapes enterprise governance, not through rogue apps, but through the approved platforms organizations deployed and trusted.
Get the full research. Understand what your security stack can’t see.
Top 20 AI tools in the workplace
What our research uncovered
In The Rise of AI Shadow IT, we set out to quantify how deep this problem really goes inside modern organizations. Building on external industry research, our analysis of real‑world activity surfaces patterns most security dashboards never show.
Our report connects these macro trends to concrete scenarios inside the enterprise — broken down by role, data type, and activity — and maps them directly to insider risk, data exfiltration, and compliance exposure.
Why employees are leading the AI charge
Employee demand is not hypothetical — it’s already the norm. One IBM‑sponsored study found 80% of American office workers use AI in their roles, yet only 22% rely exclusively on employer‑provided tools. Another survey from WalkMe shows 78% of employees use unapproved AI and just 7.5% have received extensive AI training.
Workers push into shadow AI for simple reasons:
- Official AI tools feel slow to arrive or too limited for real work.
- 53% of knowledge workers say they use their own AI tools because they prefer the independence, and 33% say IT doesn’t offer what they need.
- In many organizations, fewer than half of employees even understand the AI usage policy.
In other words, shadow AI is not driven by malicious insiders; it’s driven by ambitious employees trying to hit targets with the best tools they can get.
Employees value AI productivity, while organizations often lack the visibility needed to govern it safely.
The quiet data exposure problem
While intent may be benign, the data exposure is not. Unapproved AI use creates new, largely invisible channels where sensitive information leaves your environment:
Because these actions rarely show up in sanctioned app catalogs or coarse‑grained network logs, leaders underestimate how much sensitive data is being exposed and where it’s going.
Why traditional controls don’t see shadow AI
Most security stacks were not designed with AI interaction patterns in mind.
Even organizations with mature DLP, CASB, and EDR struggle to answer basic questions.
Which users are sending data to public AI tools?
What types of data are being shared — and do they include regulated information or crown‑jewel IP?
Are AI outputs being copied back into codebases, documents, or downstream systems?
AI traffic is often encrypted and routed through the browser, making simple URL blocking both brittle and over‑broad.
Binary “allow/deny all AI” rules ignore context such as user role, data classification, and business justification.
Shadow AI is fragmented across dozens of apps, plugins, and personal accounts, with one study noting 71% of workers using unapproved AI tools — and 51% doing so weekly.
Without user‑centric visibility into how individuals interact with AI and what data is involved, it’s almost impossible to craft effective, nuanced guardrails.
What is shadow AI?
On the surface, it looks harmless: a marketer drafting copy, a sales rep generating follow‑up emails, an engineer asking for code help. Underneath, three things are happening at once:
Shadow AI is any use of AI tools and services outside official oversight — tools employees adopt on their own, without security review, procurement, or governance. One global study of 6,000 knowledge workers found that 50% of all employees are shadow AI users, relying on non‑company AI tools to get work done.
- Unapproved AI apps are being connected to live business data
- Sensitive content is being pasted into prompts or uploaded as files
- AI outputs are flowing back into decisions, code, and customer communications
Because these behaviors happen in the browser, at the endpoint, and in personal accounts, they often sit completely outside existing security visibility.
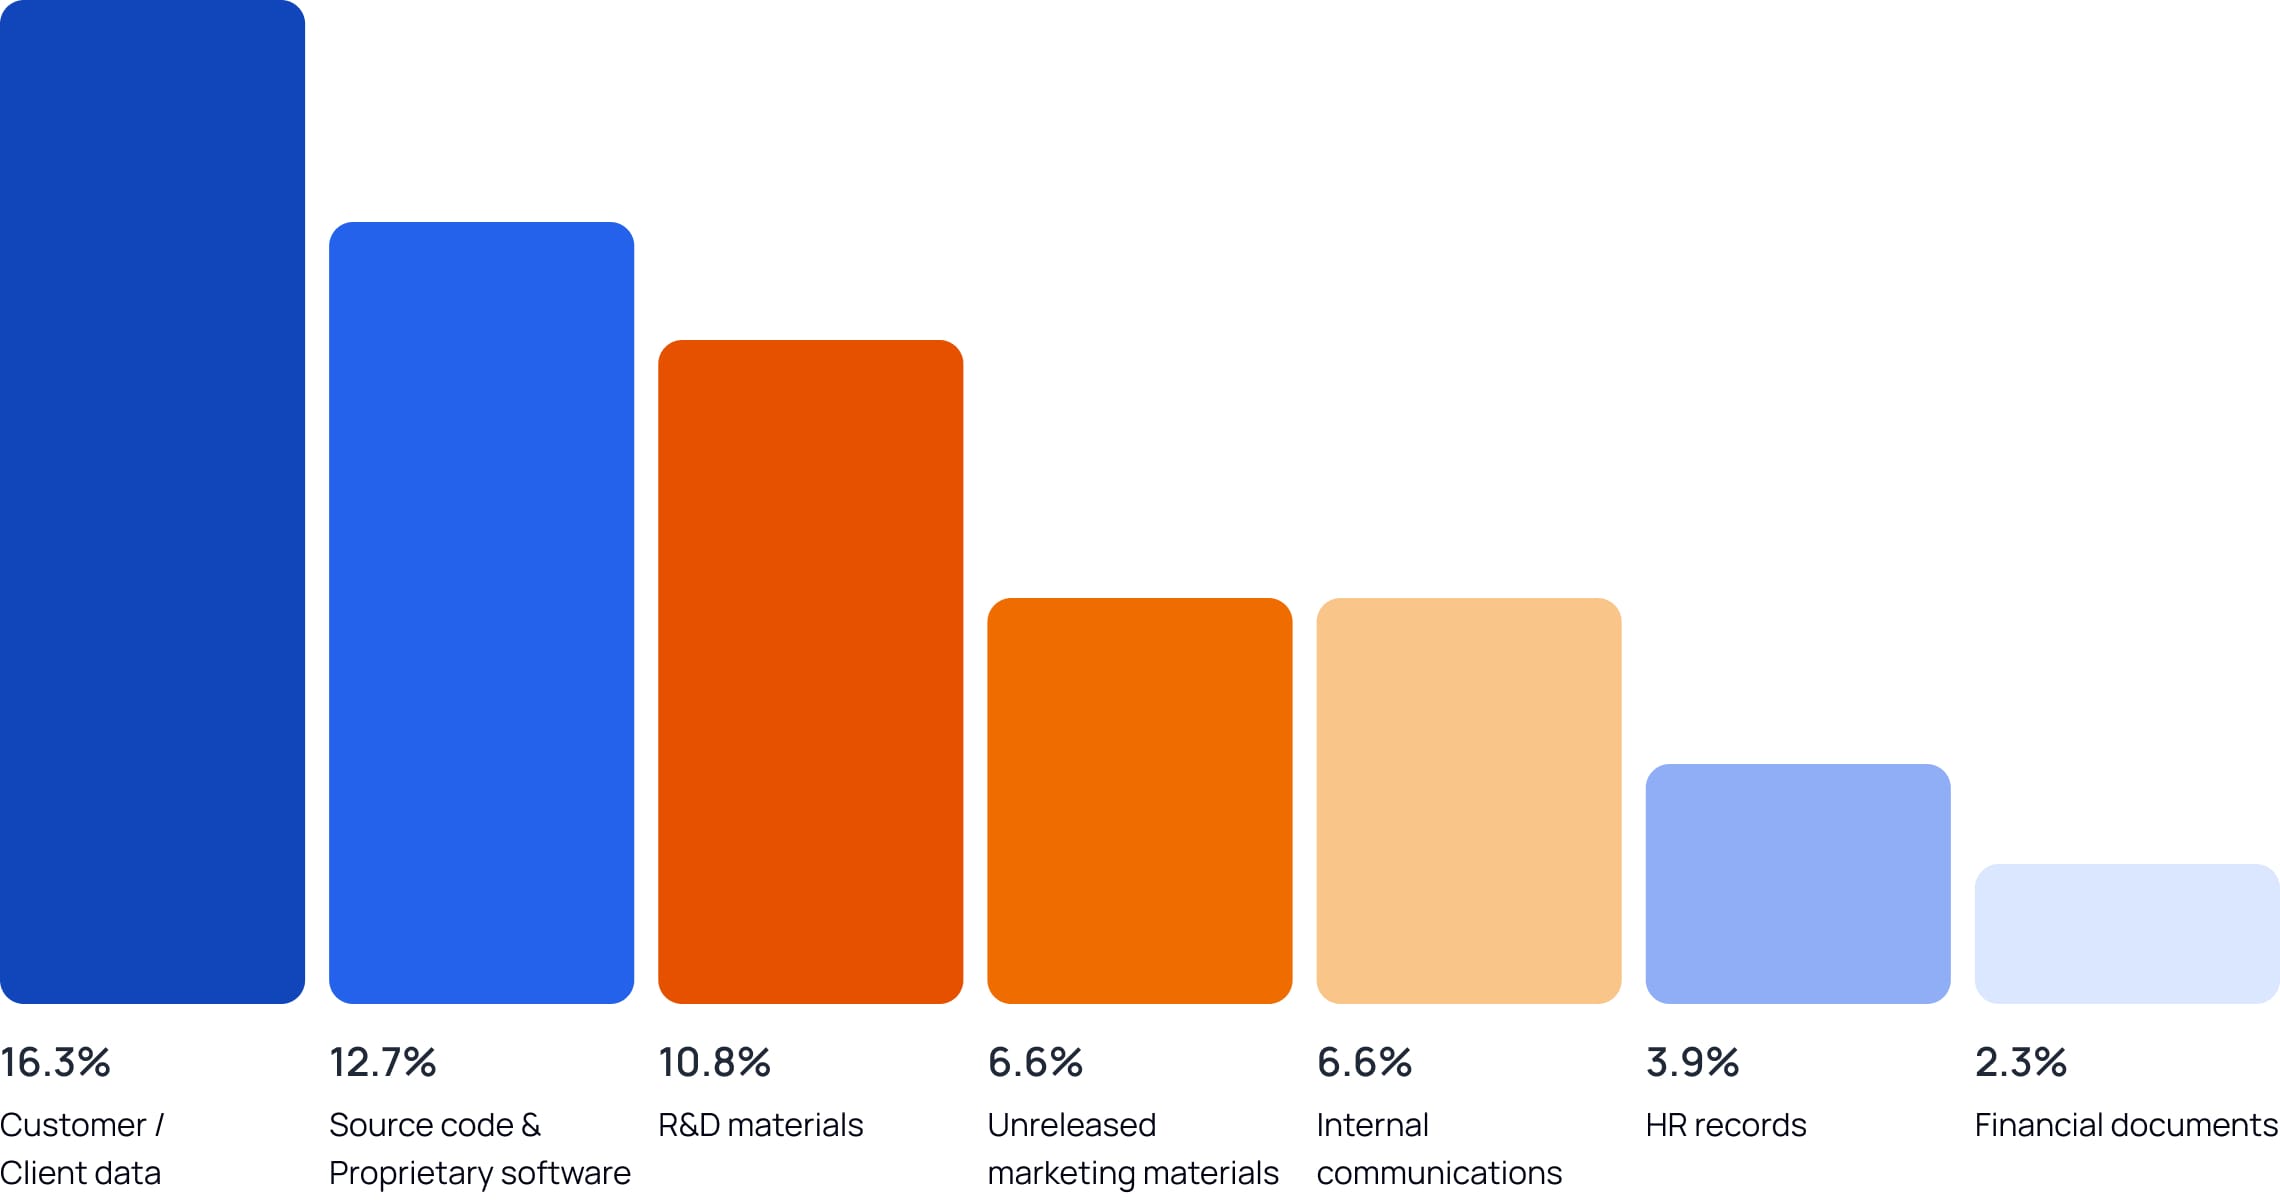
Sensitive Data Categories Entering AI Tools
Customer data, source code, and R&D materials represent the largest measured categories.
A practical playbook for security and risk leaders
The good news: you don’t have to choose between innovation and protection.
Organizations making real progress against shadow AI follow a pattern you can replicate.
In the report, we outline a pragmatic four‑step approach.
Move beyond app‑level inventories to user‑level telemetry that shows who uses AI, which tools they touch (sanctioned and unsanctioned), and what types of data move in and out of those interactions.
Classify AI activity by sensitivity, business function, and risk impact so you can distinguish acceptable experimentation from activities likely to expose regulated or highly confidential information.
Replace blunt blocking with contextual policies that consider user role, device posture, data classification, and destination — guiding employees at the moment of use rather than relying solely on static training.
Provide secure, enterprise‑grade AI options — backed by focused training — so employees are less tempted to lean on risky personal tools. When almost 80% of employees are already using AI, enablement plus governance is more realistic than prohibition.
Our research underscores that shadow AI is fundamentally a visibility and behavior problem, not just a tooling problem.
Download the report
The Rise of AI Shadow IT
Shadow AI is already reshaping how your employees work — whether you can see it yet or not. The real question for security, risk, and compliance leaders is how quickly you can understand what’s happening and put smarter guardrails in place.
In The Rise of AI Shadow IT, you’ll get:
- Fresh data on how employees actually use AI across roles and teams
- Quantified exposure scenarios tied to AI prompts, uploads, and plugins
- A step‑by‑step blueprint to regain visibility and control without slowing innovation